Blog
What the SR 2026 Delay Actually Means for Your ISO 20022 Roadmap
Swift’s SR 2026 delay changes the ISO 20022 roadmap. Learn what banks need to do now on structured addresses, compliance, data quality and migration.
Read More

As cloud infrastructure becomes increasingly complex and dynamic, Infrastructure as Code (IaC) has become a foundation of DevOps and cloud-native development. Terraform, a popular IaC tool developed by HashiCorp, allows teams to define cloud resources using simple, declarative code. However, with great power comes great responsibility and security often gets overlooked in the rush to deploy.
Snyk is a powerful security tool designed to identify misconfigurations and vulnerabilities in IaC files before they are deployed. Snyk is a developer-first security platform that integrates seamlessly into your development workflow, enabling teams to find and fix vulnerabilities in real time. Unlike traditional security tools that often slow down development, Snyk fits naturally into DevOps processes, providing clear, actionable insights without disrupting delivery speed. Its real-time scanning capabilities and automated fixes allow teams to address issues early in the software development lifecycle—making security a shared responsibility between Dev and security teams. When paired with Terraform, Snyk becomes a crucial part of a modern DevSecOps pipeline, allowing teams to ship infrastructure confidently, securely, and at scale.
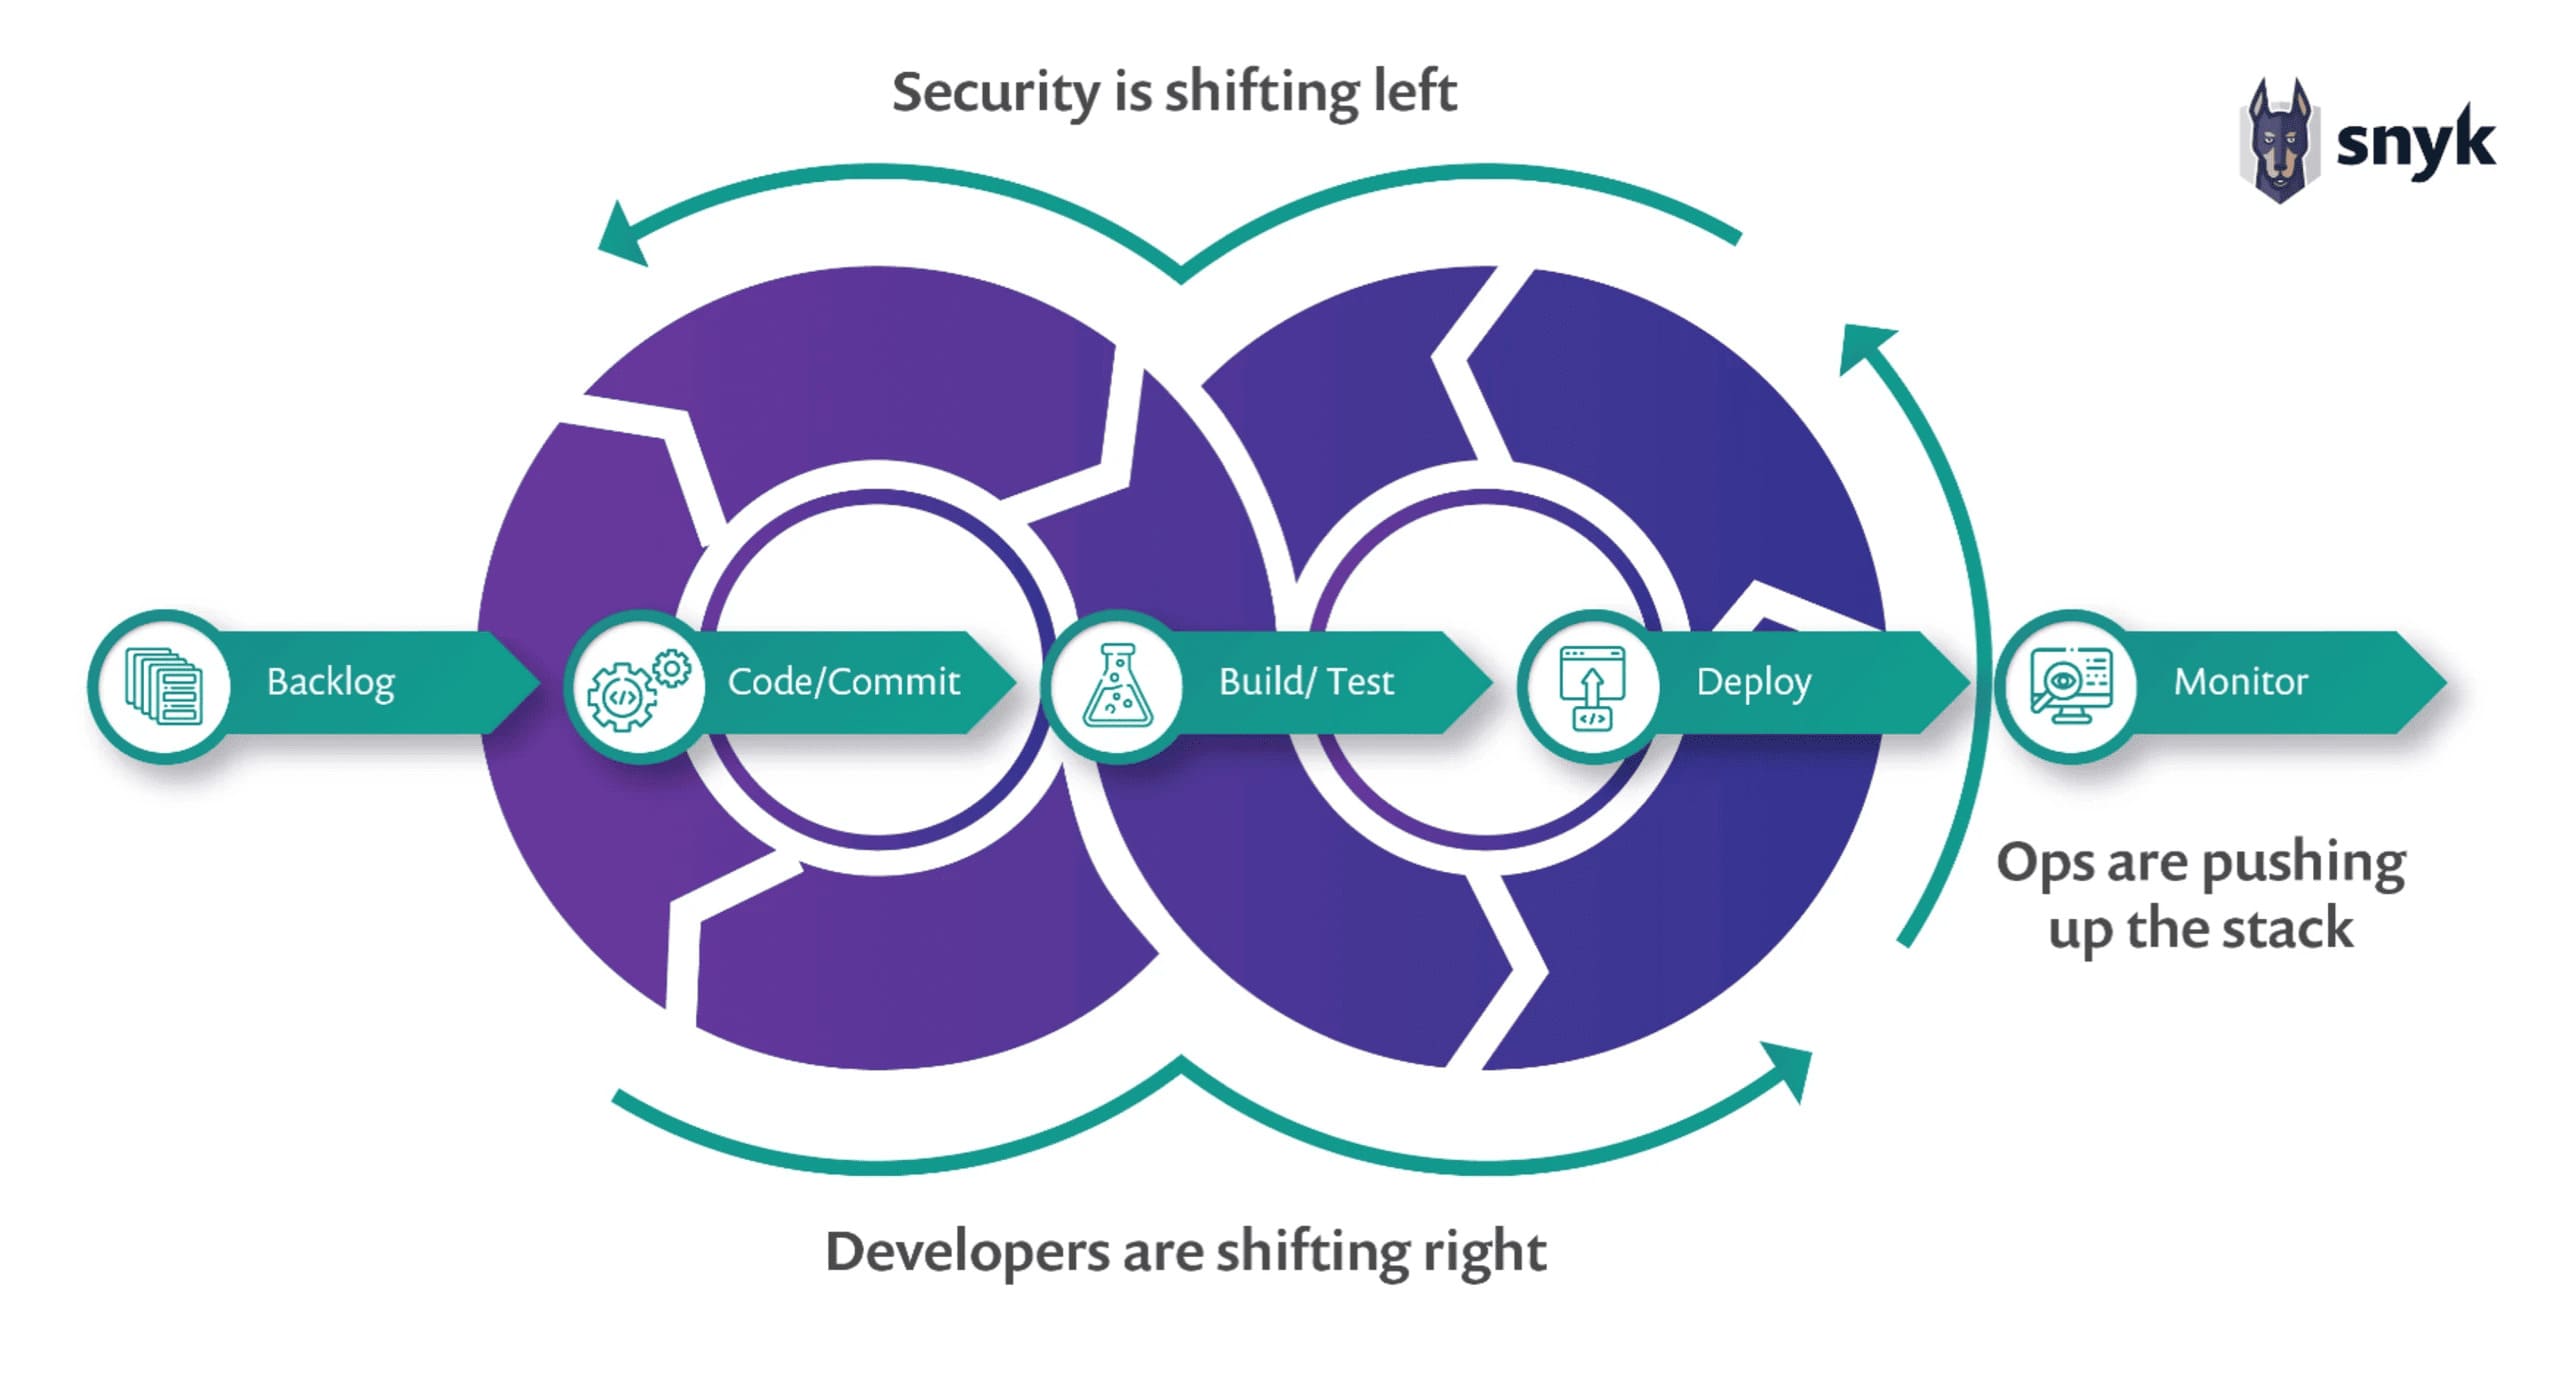
Infrastructure-as-Code enables automation, repeatability, and version control for cloud resources. But it also creates a new attack surface. Misconfigured Terraform files can inadvertently:
Since IaC defines how cloud infrastructure behaves, any misconfiguration in code gets reproduced every time the configuration is applied. This makes it vital to catch security issues early, preferably at the development stage — a key principle of shift-left security.
Snyk IaC is built to scan Terraform files (as well as other formats like Kubernetes YAML and CloudFormation) for misconfigurations that could lead to security or compliance risks.
Here’s how it fits into a secure DevOps workflow:
Snyk helps make security a developer-friendly concern, not a bottleneck that appears after infrastructure is deployed.
Key Features of Snyk IaC for Terraform
Scanning Terraform code with Snyk in GitHub Action
Integrating Snyk into GitHub Actions lets you automatically scan Terraform code for misconfigurations and security issues whenever changes are pushed. This approach adds an essential security layer early in your CI/CD pipeline.
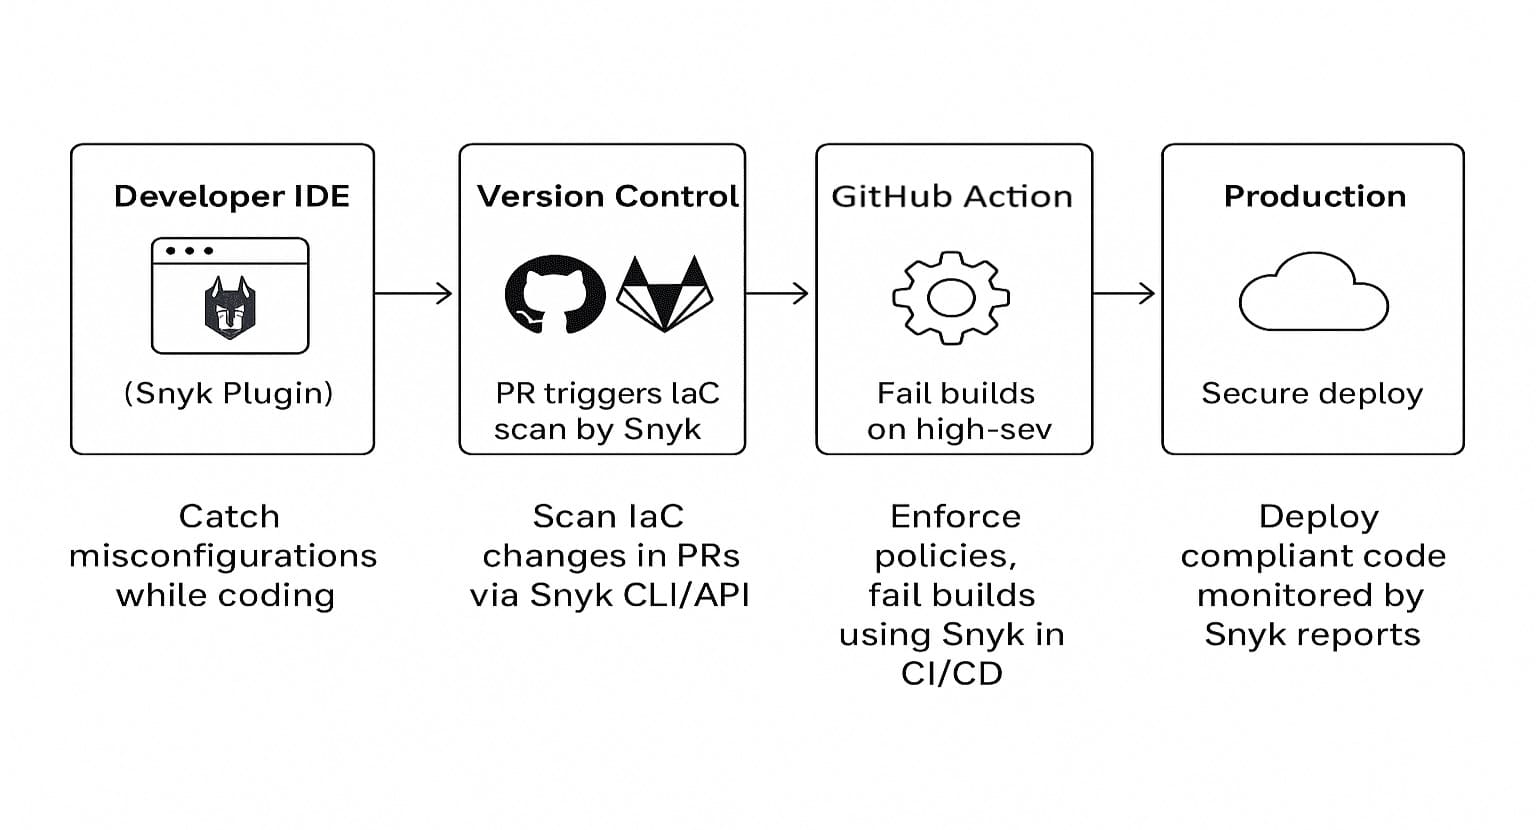
Below GitHub action workflow is configured to run the workflow each time new code is pushed in the repository. The workflow uses snyk test to scan your Terraform files for both security vulnerabilities and misconfigurations issues and then uploads a result to GitHub Security Code Scanning.
Swift’s SR 2026 delay changes the ISO 20022 roadmap. Learn what banks need to do now on structured addresses, compliance, data quality and migration.
Code generation got fast. Getting an autonomous workflow into a bank’s production control environment did not. In Banking & Financial Services (BFS), the blocker is rarely the model; it’s trust. A risk officer will not sign off on a system that cannot say why it flagged something, that does its arithmetic inside a language model, or that leaves no audit trail an examiner can open. That is exactly the gap most agentic pilots die in.
Over the last two quarters, we built a portfolio of ten BFS agentic offerings on Alti AIOS™, Altimetrik’s AI Operating System, and deployed them on two stacks: Google Cloud with Gemini and AWS with OpenAI. This piece is the architecture and design principle behind them.
Most organizations can tell you what CVEs they found last quarter. Few can tell you which packages will become a problem next month or which AI skills are running in production without a certified identity. This piece is about closing that gap.
