The Evolution of NIST Cybersecurity Framework: Transitioning from 1.1 to Draft 2.0
Share
What is the Framework?
The Framework is voluntary guidance, based on existing standards, guidelines, and practices for organizations to better manage and reduce cybersecurity risk. In addition to helping organizations manage and reduce risks, it was designed to foster risk and cybersecurity management communications amongst both internal and external organizational stakeholders.
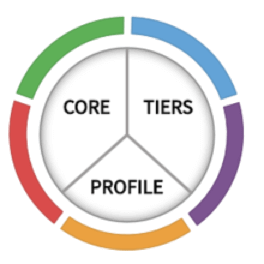
The Cybersecurity Framework Components: Core, Implementation Tiers, and Profiles
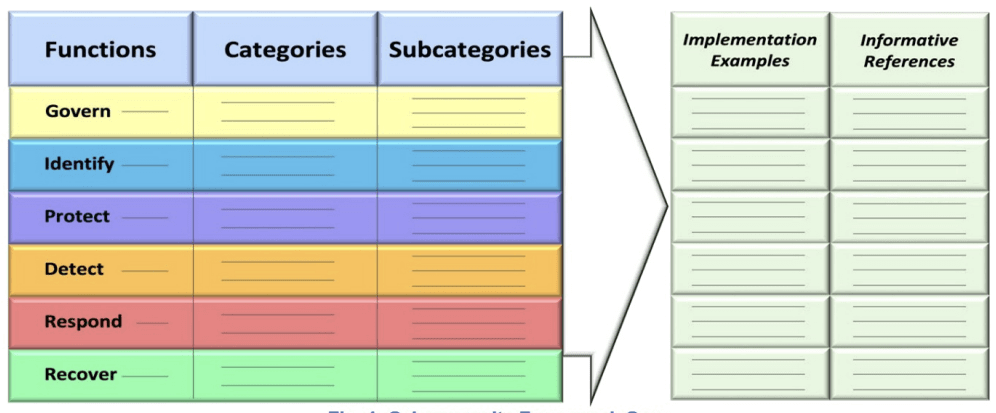
The Framework Core provides a set of desired cybersecurity activities and outcomes using common language that is easy to understand. The Core guides organizations in managing and reducing their cybersecurity risks in a way that complements an organization’s existing cybersecurity and risk management processes.
The Framework Implementation Tiers assist organizations by providing context on how an organization views cybersecurity risk management. The Tiers guide organizations to consider the appropriate level of rigour for their cybersecurity program and are often used as a communication tool to discuss risk appetite, mission priority, and budget.
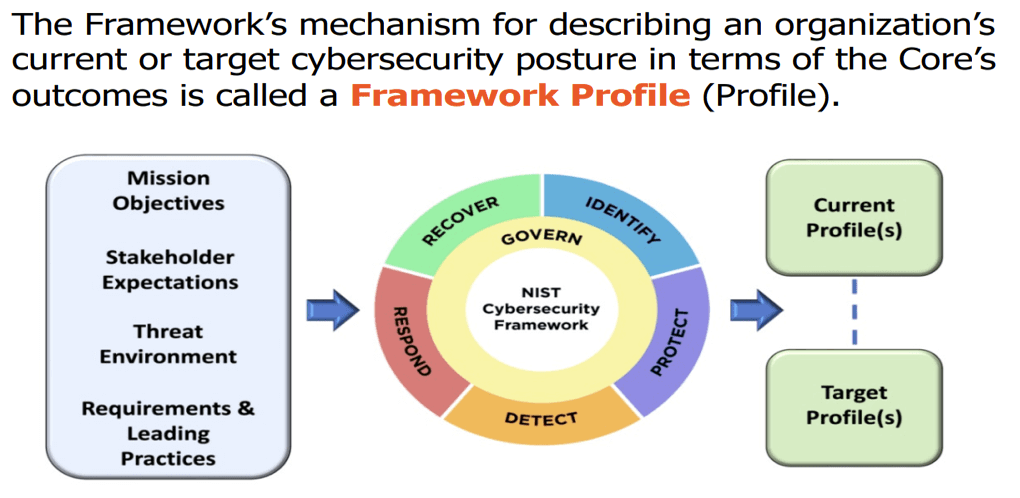
Framework Profiles are an organization’s unique alignment of their organizational requirements and objectives, risk appetite, and resources against the desired outcomes of the Framework Core. Profiles are primarily used to identify and prioritize opportunities for improving cybersecurity at an organization.
Why is NIST deciding to transition from the Framework 1.1 to CSF 2.0?
The NIST Cybersecurity Framework was intended to be a living document that is refined, improved, and evolves over time. These updates help the Framework keep pace with technology and threat trends, integrate lessons learned, and move best practice to common practice. NIST first produced the Framework in 2014 and updated it in April 2018 with CSF 1.1. Based on stakeholder feedback, and with a motive to include wider business verticals due to change in cybersecurity landscape and to help organizations more easily and effectively manage cybersecurity risk, NIST is working on a new, more significant update to the Framework: CSF 2.0.
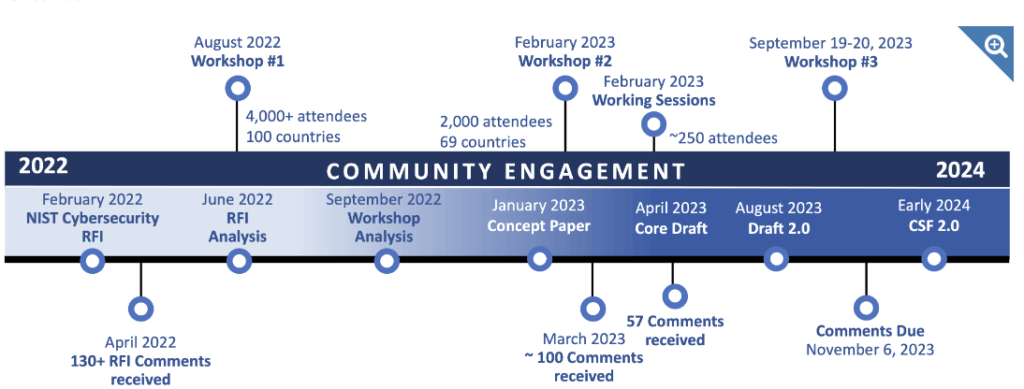
Currently we are at below step and final version will be release by early 2024
There are significant updates introduced on CSF draft 2.0:
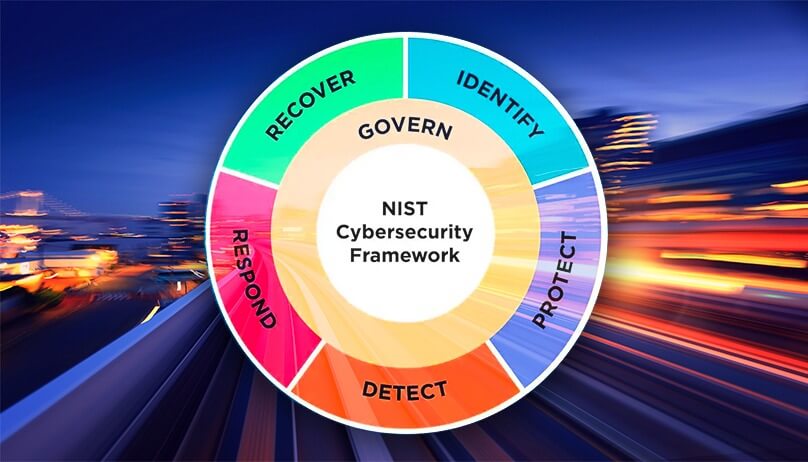
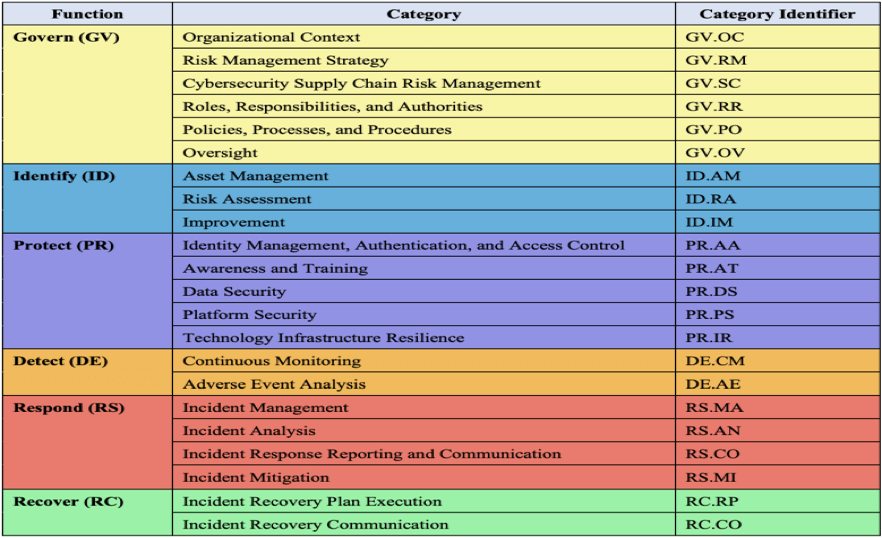
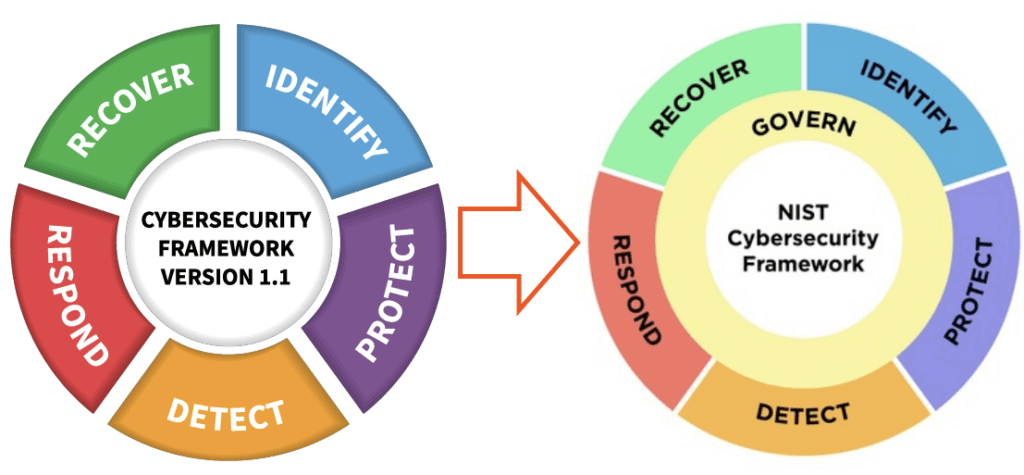
New Function introduced i.e. Govern, and changes in the Category and Subcategories
Increased guidance on CSF implementation (Profiles and implementation Examples)
Current and Target Profiles
Implementation Examples
Clarified understanding of cybersecurity measurement and assessment (see also NIST SP 800-55)
Emphasized cybersecurity supply chain risk management (C-SCRM) (see also NIST SP 800-161r1)
Alignment (and integration) with other Frameworks and standards. New references will be added later.
Recognition of the broad use of the Framework (New Title and wider scope to include small businesses)
CSF 1.1
Title:“Framework for Improving Critical Infrastructure Cybersecurity”
CSF Draft 2.0
Title: “The NIST Cybersecurity Framework 2.0”
A new function “Govern” is Introduced
The framework (2.0) can be used to understand, assess, prioritize, and communicate about cybersecurity risks:
Understand and Assess:
Describe an organization’s current or target cybersecurity posture within and across organizations, sectors, or business units.
Determine where an organization may have cybersecurity gaps, including with respect to existing or emerging threats or technologies, and assess progress toward addressing those gaps.
Align policy, business, and technological approaches to managing cybersecurity risks across an entire organization or in a more focused area, such as a portion of the organization, a specific technology, or technology suppliers.
Prioritize:
Prioritize opportunities to improve cybersecurity risk management.
Identify, organize, and prioritize actions for reducing cybersecurity risks that align with the organization’s mission, legal and regulatory requirements, and risk management and governance expectations.
Inform decisions about cybersecurity-related workforce needs and capabilities.
Provide a common language for communicating with internal and external parties about cybersecurity risks, capabilities, needs, and expectations.
Complement an organization’s risk management process by presenting a concise way for executives and others to distil the fundamental concepts of cybersecurity risk so that they express at a high-level risk to be managed and how their organization uses cybersecurity standards, guidelines, and practices.
Conclusion:
NIST CSF 2.0 will become a milestone for a robust security framework of any organization. It has become more granular and easier to understand & implement. More n more cyber security professional will take advantage of it. Security Professionals are eagerly waiting for final version that will be released by early 2024.